A mobile app can feel secure the moment it launches. But once it reaches a customer’s phone, it enters a world the business cannot fully control. The app can be examined, manipulated, or attacked while it is running, often without the customer ever knowing. Founded in 2010 and headquartered in Tokyo, Japan, SecIron addresses this challenge with continuous mobile application security, helping businesses find weaknesses early, harden applications before they reach users, and maintain visibility when threats emerge on real devices.
“Mobile security is a continuous lifecycle,” says Nicole Ban, Founder and Chief Operating Officer at SecIron. The company applies this approach through three connected security layers. IronSCAN checks mobile applications for security weaknesses before release and guides to address them early. IronWALL hardens the compiled application without source-code changes or lengthy SDK integration, making reverse engineering, code tampering, runtime attacks, decompilation, and application cloning harder. Once the application reaches customers, IronSKY provides runtime visibility through behavioral detection, security analytics, and policy-based response. Together, the layers give security teams visibility from development through real-world use.
“The best security is the security that always stays on,” says Nicole. Continuous protection does not mean treating every warning as a threat. A rooted device, for example, may not indicate fraud on its own. When rooting appears alongside hooking, screen manipulation, injection, or other suspicious behavior, the level of risk can change. SecIron looks at these signals together so teams can make a more informed decision.
“Our objective is not simply ‘detect more.’ It is to make better risk decisions while protecting the customer experience,” says Nicole. That distinction matters when security becomes part of everyday business. If a control slows an app, blocks genuine customers, or produces too many false alarms, teams may eventually weaken it. SecIron focuses on protection that can remain active without getting in the way of legitimate users.
The company also works alongside the security investments enterprises already have. Businesses may maintain strong controls across networks, servers, endpoints, identity, and fraud, while the mobile application remains a blind spot because it operates on a customer-owned device. SecIron extends visibility into that space. Its technology can fit into CI/CD workflows, while mobile threat information can connect with SIEM and incident-management platforms, bringing mobile activity into existing security processes.
A digital banking environment in Hong Kong shows why such visibility matters. The organization already had server-side security controls, but suspicious activity could occur on a customer’s device while authentication, network, and transaction systems continued to see what appeared to be a legitimate session. Malware could use overlays, credential interception, screen manipulation, or other runtime interference without the full picture being visible from the server side.
SecIron applied its three-layer model to the environment. IronSCAN assessed the application, IronWALL added protection without source-code modification, and IronSKY provided runtime visibility with policy-based responses according to risk. The approach gave the security team additional device- and application-level context while requiring little developer time. The organization also passed its HKMA audit with zero findings.
“Assessment tells you the weak point; hardening makes the application harder to attack. Runtime intelligence tells you what is happening now,” says Nicole. The case shows why protection before release and visibility after deployment need to work together.
SecIron describes its approach through five ideas: coverage, simplicity, resilience, context, and proximity. The company connects assessment, application protection, and runtime monitoring rather than treating them as separate controls. Its codeless hardening can be deployed by most customers within 10 minutes or less. Layered protection is designed to defend the application as well as the security mechanisms protecting it, while multiple signals give teams more context when deciding how to respond. Its presence across Asia Pacific also helps the company understand different security needs, regulatory expectations, and operating conditions.
The threat environment continues to change. Attackers are becoming faster and more automated, while AI is accelerating the development of new attack techniques. SecIron is developing AI-assisted threat analysis to help security teams turn large volumes of telemetry into faster, more useful decisions. It is also strengthening detection against advanced device manipulation and root-hiding techniques, where static blacklists can struggle to keep pace.
“The advantage will increasingly come from who can adapt faster,” says Nicole. That idea shapes the company’s future plans. SecIron intends to expand into areas such as API security, IoT, and embedded environments while making deeper use of AI in security operations. It also plans to strengthen threat intelligence and behavioral analytics and continue growing across Asia Pacific, alongside selected markets such as India and the Middle East.
The company is also watching the connection between cybersecurity and digital identity. Deepfakes, synthetic identities, emulators, and manipulated device environments are making identity alone less sufficient for judging trust. The device and application environment surrounding a user can provide another important part of the picture.
Mobile security ultimately has to work where the customer is. Protection that creates too much friction may not remain in use, while protection that cannot see activity on the device leaves an important gap. SecIron’s approach brings those concerns together, keeping security practical while giving teams greater visibility into what happens beyond the traditional enterprise perimeter. As mobile applications become central to everyday digital services, protection must continue beyond release and into real-world use. For SecIron, keeping security on means making that protection useful, adaptable, and sustainable.
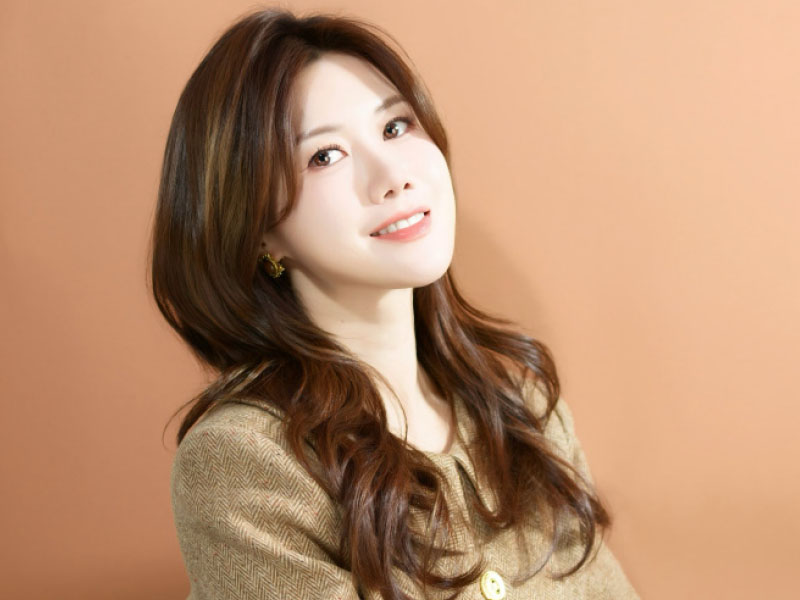
Nicole Ban, Founder & COO
seciron.com
“Our objective is not simply ‘detect more.’ It is to make better risk decisions while protecting the customer experience”